Cybersecurity and resilience, without the paperwork
Your company, more secure and ready for when something fails
Almenara tells you in time what needs attention: the supplier nobody has reviewed, the evidence about to expire, the process without a plan. And it keeps every piece of evidence, with its author and date, for any audit.
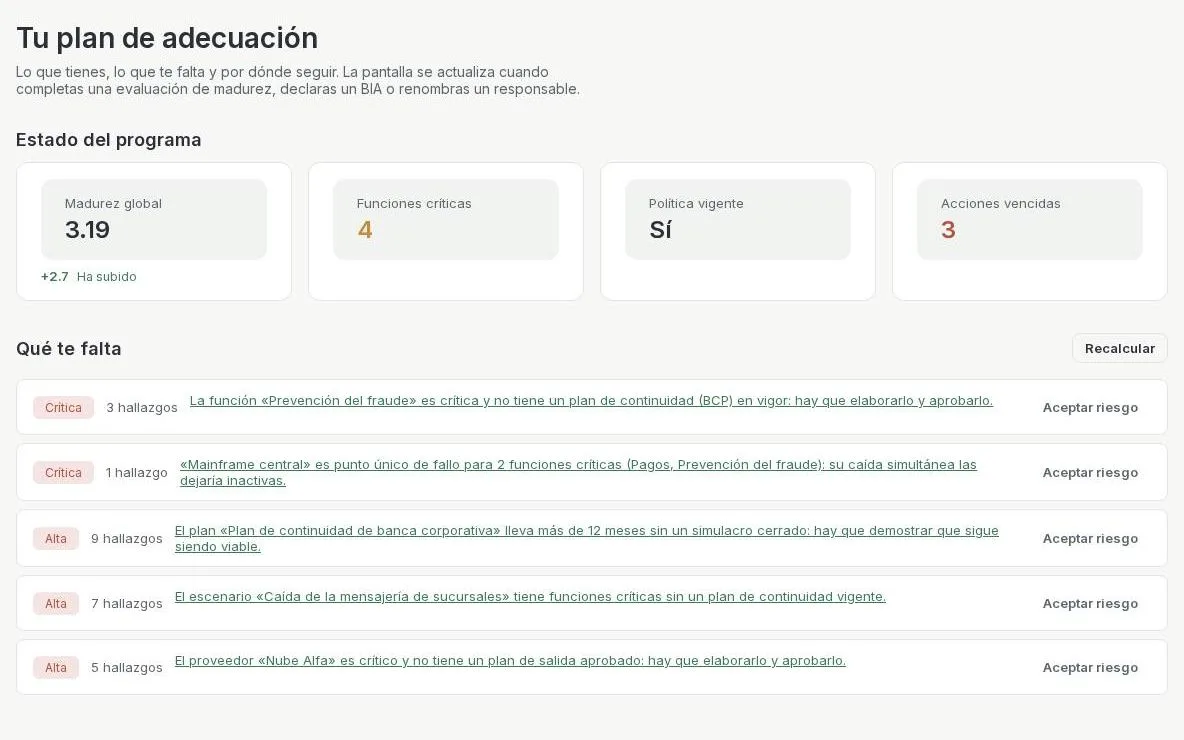
Sample data
If this sounds familiar
Three moments when Almenara makes the difference
- 01 · Cybersecurity
A supplier with access to your systems hasn't been reviewed in a year and nobody knows what safeguards it has.
Every supplier has its criticality, its questionnaire and its evidence, and Almenara warns you when something expires or gets worse. You see where a problem could get in before it does.
See the suppliers module - 02 · Resilience
A critical service goes down and nobody knows how long the business can hold out or who has to do what.
Your impact analysis says what depends on what, how long each process can be down and which plan kicks in. And you rehearse it with exercises before you need it.
See the continuity module - 03 · Time
Your CISO spends the week chasing evidence by email instead of improving security.
Each piece of evidence is uploaded once, with its owner and its date, and counts for every control that asks for it. What expires flags itself and reports come out of the platform.
See the compliance module
And compliance comes out of that same work: ISO 27001, ENS, DORA, NIS2 or the questionnaire a client sends you, with the same evidence. See the framework catalogue
Demo · Your cloud provider goes down
Your cloud provider goes down. This is what you see in Almenara.
A whole case, from the first alert to the report prepared for your lead to review and send. Six steps, on sample screens and without talking to anyone.
- 09:12The provider’s notice arrives linked to its record.
- 09:12You see which functions stop and how long each one can hold out.
- 09:40Your lead classifies it and knows which reports are due and when.
- 09:44The continuity plan kicks in, with a person in charge of each task.
- 10:40Almenara fills in the notification; your lead reviews it and sends it.
- AfterwardsThe evidence is kept and the provider is flagged for reassessment.
Sample data
Your cloud provider
Managed database, EU region
Supplier notice, from its portal
Database service outage in the EU region
Linked to this record
3 functions depend on it
One control, one piece of evidence, every framework
You upload the evidence once and it counts for every framework that asks for it
Each framework is mapped once to Almenara’s common controls. A piece of evidence counts for every control that asks for it and, when it expires, the control goes from “demonstrated” to “declared” in every framework at once.
Evidence
Backup restore test report
Uploaded by your systems lead · valid for 12 months
Frameworks that ask for it
- ISO 27001Annex A 8.13Demonstrated
- Spain’s National Security Framework (ENS)mp.info.6Demonstrated
- DORAArt. 12Demonstrated
- NIS2Art. 21(2)(c)Demonstrated
- A customer’s security questionnairebackupsDemonstrated
Illustrative example. These are some of the frameworks available in Compliance.
Where your data lives
Your data, where you decide
The same platform, in a European Union cloud or on your own servers.
SaaS in the EU
- One virtual machine per customer, isolated from other companies’ machines.
- Hosting and backups in data centres in the European Union.
- No third party outside the EU handles your data.
- We run it: you have nothing to install or maintain.
On your servers
- It’s installed in your infrastructure: the data never leaves your premises.
- Our team handles the rollout and maintenance, coordinated with yours.
- For when your policy requires the data to stay in-house.
If you want to use a third-party AI model, you connect your own with your own key: you choose it and you contract it. If you sign in with your Google or Microsoft account, they only see your name and email when you sign in.
How we protect your dataWhat you contract
The tool and, if you need it, the team
Your team uses the platform. We deliver the services, with a fixed scope and deliverable. They are contracted separately and can be combined.
The platform: your team uses it
It organises the work, warns you about what expires and keeps every piece of evidence with its author, date and version. You start with the module you need most.
- Third partiesInventory, questionnaires and evidence
- ComplianceRisk, SoA and audits
- IncidentsLogging and on-time reporting
- ContinuityBIA, plans and exercises
SaaS or on your servers, with the same platform.
See the platformThe services: our team delivers them
For what you don't have the time or the people to do: the impact workshop, the internal audit, the register for the supervisor, an external CISO.
- Starting from scratchGap analysis against a framework · Initial supplier review · Data migration from spreadsheets
- It comes round every yearRisk assessment · Business impact analysis (BIA) workshop · NIS2 and DORA board training
- I need a plan I don’t haveBusiness continuity and recovery plan · Incident response playbooks · Supplier exit plan
- Something has happenedSupplier audit · Post-incident review
- I have no one to run itVirtual CISO · Security questionnaire responses
If you use the platform, the result stays in its module; if not, we deliver it as a report.
See the servicesYou can start with either: the platform doesn't include the services, and contracting a service doesn't commit you to the platform.
Why Almenara
Who’s behind it
- 01
Built by people who prepare audits
Our storyAlmenara comes from preparing companies for audits and for when things fail. That's why it keeps what you'll be asked for: who, when, with what evidence and in which version.
Founded by José Ramón Santos Crespo. LinkedIn profile
- 02
Independence
How we deliver servicesWe don't certify, nor do we run the internal audit of what we implement or manage. We help you prepare; an accredited body certifies.
Our certifications, in preparation
We’re preparing our own management system for ISO/IEC 27001 and ENS certification. We aren’t certified yet: when we are, you’ll see each seal here with the body that issued it.
ISO/IEC 27001In preparation
Working towards ISO/IEC 27001 with our information security management system.
ENSIn preparation
Preparing the certificate of conformity with Spain’s National Security Framework.
Frequently asked questions
Before you talk to us
- What do I do with what I already have in Excel?
- It's imported. Your supplier inventory, risk register, statement of applicability and continuity data load from Excel: what you already have isn't typed in again.
- Who in my team uses it?
- Whoever runs the management system, whoever assesses suppliers and whoever decides. Each person sees only the modules and actions of their role. Your suppliers come in through their own portal, with no licence.
- How much does it cost?
- It depends on the modules you need and whether you want it as SaaS or on your servers. In a meeting you tell us what you have, and we send you a fixed-price proposal, with the price of each part.
- What changes on audit day?
- Every control shows its current evidence, who uploaded it and when, and the per-framework reports come out of the platform. No rebuilding the year the week before.
Tell us what's worrying you
A supplier you don't control, a continuity plan nobody has tested, an audit coming up or a client's questionnaire: tell us what you have and we'll show you how it would look in Almenara.